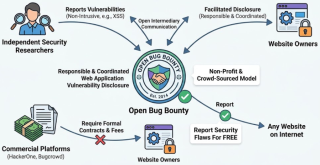
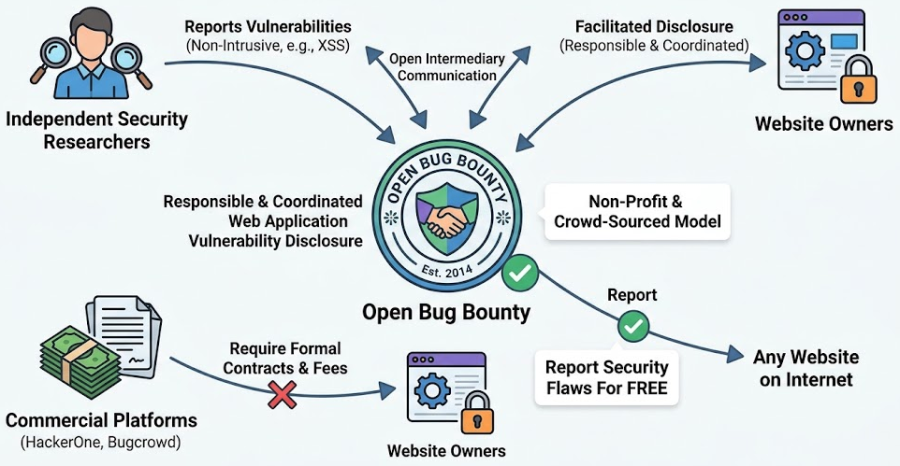
| While reviewing the site access logs, I noticed a visit from a website named openbugbounty.org. Upon looking into it, I found that the site provides a service that inspects website security vulnerabilities for free. Although it feels a bit crude when you visit the site, it is more than enough to gain insights into what weaknesses exist. Overview of Open Bug BountyOpen Bug Bounty (https://www.openbugbounty.org/) is a non-profit, crowd-sourced security platform launched in 2014. It acts as an open intermediary between independent security researchers and website owners to facilitate the responsible and coordinated disclosure of web application vulnerabilities. Unlike commercial platforms (e.g., HackerOne or Bugcrowd) that require companies to sign formal contracts and pay platform fees, Open Bug Bounty allows researchers to report non-intrusive security flaws on virtually any website on the internet for free.
Key Features and Characteristics- Non-Profit and Free Model: The platform does not charge website owners or security researchers. It operates entirely as a community-driven initiative.
- ISO 29147 Compliance: Follows international standard guidelines for vulnerability disclosure, ensuring a standard procedure for notifying website operators.
- Open Scope: Researchers can report vulnerabilities found on any public domain, provided the testing was non-intrusive and ethical.
- Reputation & Hall of Fame: Researchers build a public profile by earning reputation points, badges, and rankings based on verified vulnerability submissions.
- Voluntary Rewards: While website owners are not required to pay cash rewards, they can voluntarily award bounties, swag, or public certificates of appreciation to researchers.
Supported Vulnerability TypesOpen Bug Bounty strictly focuses on non-intrusive web vulnerabilities that can be demonstrated with a simple Proof of Concept (PoC) without harming the website or accessing sensitive data. Allowed Vulnerabilities- Cross-Site Scripting (XSS): Reflected, Stored, and DOM-based.
- Open Redirect: Unvalidated redirects and forwards.
- Cross-Site Request Forgery (CSRF): State-changing actions performable without user authorization.
- Local / Remote File Inclusion (LFI / RFI): Path traversal issues that do not disrupt operations.
- Security Misconfigurations: Publicly exposed sensitive configuration files or headers.
Disallowed / Prohibited Vulnerabilities- Invasive Vulnerabilities: SQL Injection (SQLi), Remote Code Execution (RCE), Command Injection (unless purely non-intrusive PoC).
- Service Disruption: Denial of Service (DoS/DDoS) attacks.
- Social Engineering: Phishing, spam, or physical security testing.
- Automated Mass Scans: Submissions resulting from noisy, automated vulnerability scanners without manual verification.
How the Disclosure Process Works- Vulnerability Discovery: A security researcher discovers a non-intrusive vulnerability on a website.
- Report Submission: The researcher submits the details (including the URL and PoC) to Open Bug Bounty. The technical details remain hidden from the public.
- Owner Notification: Open Bug Bounty automatically attempts to contact domain owners via
security.txt, WHOIS email records, abuse contacts, or platform notifications. - Patching & Verification: The website owner receives the report, fixes the security flaw, and marks the report as resolved.
- Public Disclosure: Once verified as fixed (or after a standard disclosure deadline), public summary details are released, and the researcher receives public credit on their profile.
Ethical Guidelines and RulesTo prevent abuse and maintain legal compliance, Open Bug Bounty enforces strict policies: - Zero Extortion: Researchers are strictly forbidden from demanding money, gift cards, or compensation in exchange for vulnerability details. Doing so results in an immediate permanent ban.
- No Data Theft: Accessing, downloading, modifying, or deleting user data or server files is strictly prohibited.
- Privacy Maintenance: Researchers must keep vulnerability details confidential until the site owner resolves the issue or the disclosure grace period expires.
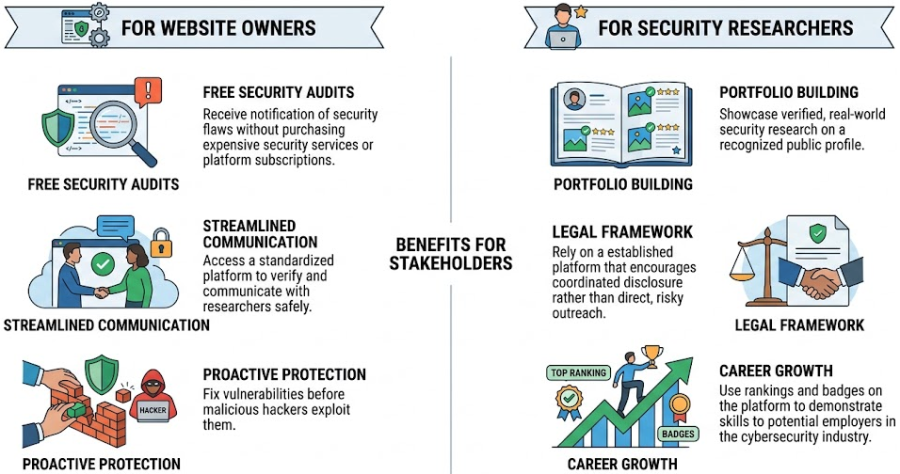
Benefits for StakeholdersFor Website Owners- Free Security Audits: Receive notification of security flaws without purchasing expensive security services or platform subscriptions.
- Streamlined Communication: Access a standardized platform to verify and communicate with researchers safely.
- Proactive Protection: Fix vulnerabilities before malicious hackers exploit them.
For Security Researchers- Portfolio Building: Showcase verified, real-world security research on a recognized public profile.
- Legal Framework: Rely on a established platform that encourages coordinated disclosure rather than direct, risky outreach.
- Career Growth: Use rankings and badges on the platform to demonstrate skills to potential employers in the cybersecurity industry.
|